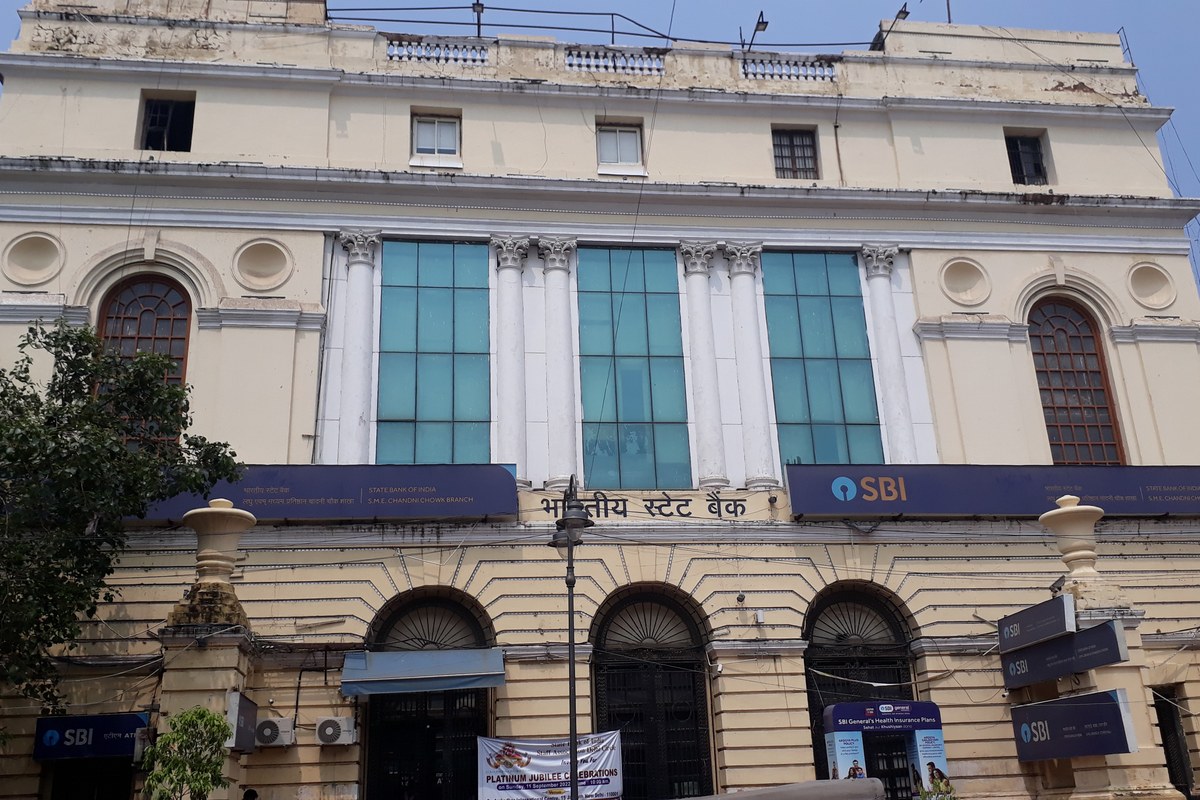
State Bank of India (SBI) told the stock exchanges on Wednesday, October 21, that it had “experienced an incident involving the loss of certain data”. A preliminary analysis of about 3.75 lakh records found on the dark web identified 3,897 SBI customer records containing personally identifiable information. The bank said it was alerted on October 16 by its threat intelligence provider, the Defence Cyber Agency and CERT-In, the national cyber security agency.
According to the filing, the exposed information reportedly included customers’ registered mobile numbers, dates of birth, names, gender, email addresses and residential addresses, along with branch and CIF (customer information file) identifiers, lead IDs and metadata linked to loan or lead records. The filing does not list passwords, PINs, OTPs or card numbers. Nor does it say how the data left the bank or what the rest of the records contain, Hindustan Times noted.
The claim first surfaced on X. Digital rights group Internet Freedom Foundation (IFF) said a threat-monitoring account flagged a group calling itself “Siriusim”, which claimed to have released 3.75 lakh rows of SBI data and 2,722 PDF documents, including loan applications. SBI’s filing does not mention documents, and the claims have not been independently verified.
SBI says it has activated its incident response protocols and hired an independent CERT-In-empanelled agency to establish whether the data is authentic, where it came from and how far the exposure goes. Later on Wednesday, it posted a note saying the incident had affected “a very very small number of customers”.
“Customer balances are completely safe and we are taking all possible steps to protect the interests of our valued customers,” SBI said in the note it posted on X.
View @TheOfficialSBI’s post on X
The main risk flagged so far is fraud. IFF warned that people whose phone numbers, dates of birth and addresses were exposed could be targeted by fraudsters posing as bank officials. SBI’s own cyber security guidance says the bank never asks for your user ID, passwords, card number, PIN or CVV, and that you should not share an OTP, ATM PIN or CVV over the phone. Its advice: verify a caller’s identity, don’t install software on a stranger’s advice, and look up helpline numbers only on the official website. Cyber incidents can be reported to report.phishing@sbi.co.in, on the national cyber crime helpline 1930, or at cybercrime.gov.in.
It is unclear whether SBI has told affected customers individually; the bank did not respond to The Indian Express on this. IFF has asked SBI to notify each of them, noting that the breach-notification duty in the Digital Personal Data Protection Act, 2023 takes effect only on May 13, 2027. SBI says a detailed assessment is under way.
More to read
Behind the story
Read the sources and explore the context for yourself.
- State Bank of India: Disclosure under Regulation 30 of SEBI (LODR) – incident involving data loss, filed with BSE (21 Oct 2026)bseindia.com
- The Economic Times: SBI flags dark web exposure of 3,897 customer records (21 Oct 2026)economictimes.indiatimes.com
- Hindustan Times: SBI flags ‘loss of certain data’ as 3,897 customer records surface on dark web (21 Oct 2026)hindustantimes.com
- India Today: Cyberattack impacted very small number of customers, balances completely safe: SBI (21 Oct 2026)indiatoday.in
- State Bank of India (@TheOfficialSBI) on X, 21 Oct 2026: “Important Information for Customers”x.com
- State Bank of India: Cyber Security – Be Aware & Stay Protected from Cyber Fraudssbi.bank.in
- State Bank of India (@TheOfficialSBI) on X, 20 Oct 2026: official customer care numbersx.com
- The Indian Express: SBI data leak explained: What customer information was exposed online? (21 Oct 2026)indianexpress.com